
Passwordless Identity Security for Financial Services
Identity security for financial services starts with phishing-resistant MFA and passwordless access to sensitive systems, and it helps meet DORA requirements.

Financial security challenges & compliance
Identity and access management (IAM) in financial services must protect sensitive information while keeping everyday work practical for tellers, advisers, and IT teams.

Growing phishing & MitM threats
A convincing sign-in page can capture passwords and relay one-time codes to a real banking service. Adding a second step does not stop these attacks if the authentication method remains phishable.

Shared workstations & unattended PCs
At branch counters and operations desks, an open session can give the next person access under a colleague's account. Shared devices need individual authentication and reliable locking when staff step away.

Legacy banking apps & employee friction
Older applications may still require separate credentials and lack SAML or OIDC support. Repeated logins slow employees down, while replacing a critical banking system solely to modernize authentication can be impractical.

Evolving regulatory compliance
Where PCI DSS or DORA applies, teams need evidence of appropriate authentication, access restrictions, and monitoring. Meeting those obligations also requires documented procedures and regular reviews of who can access sensitive systems.
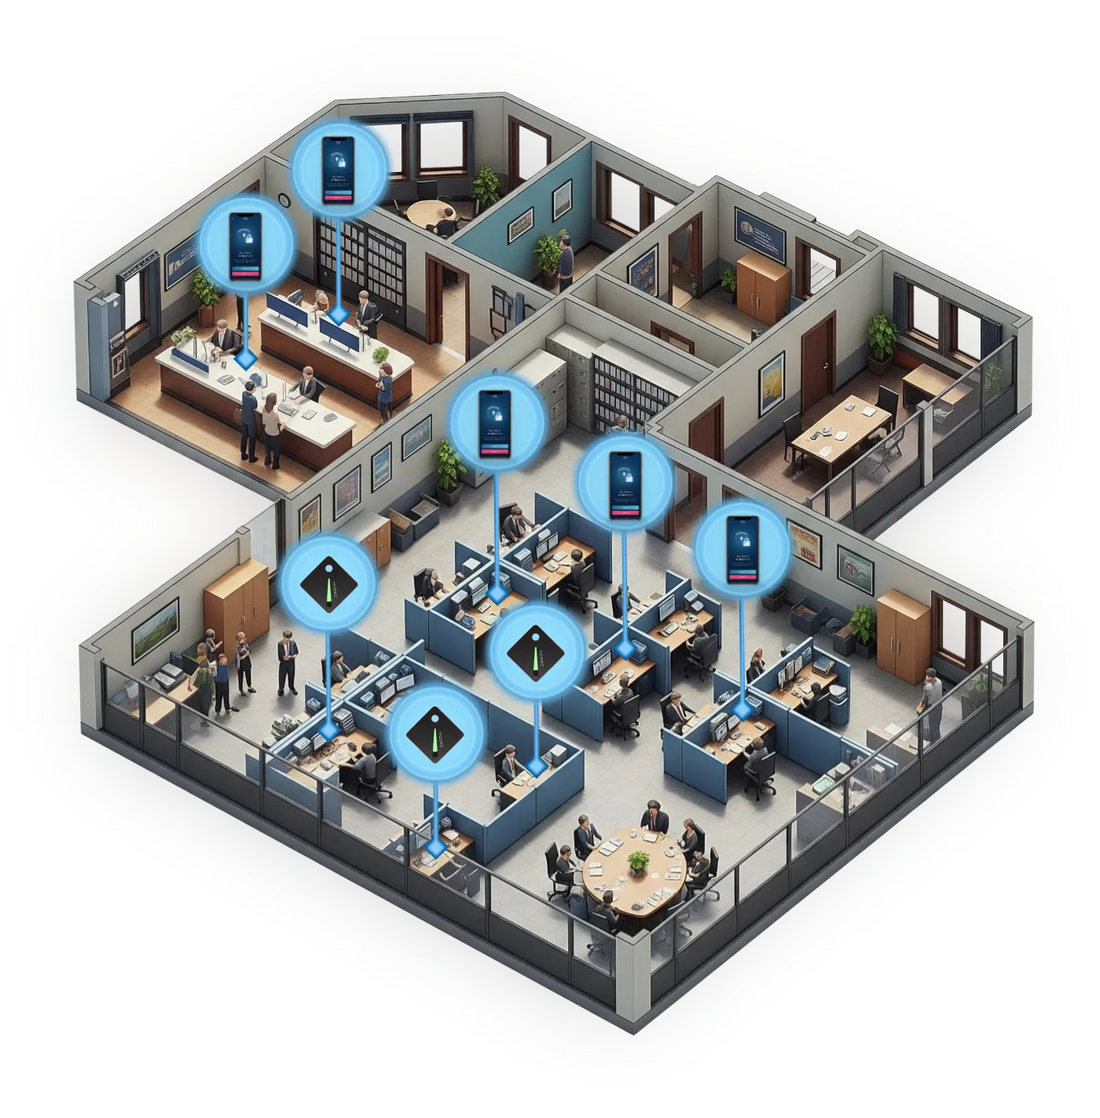
Passwordless IAM Solutions for Financial Services
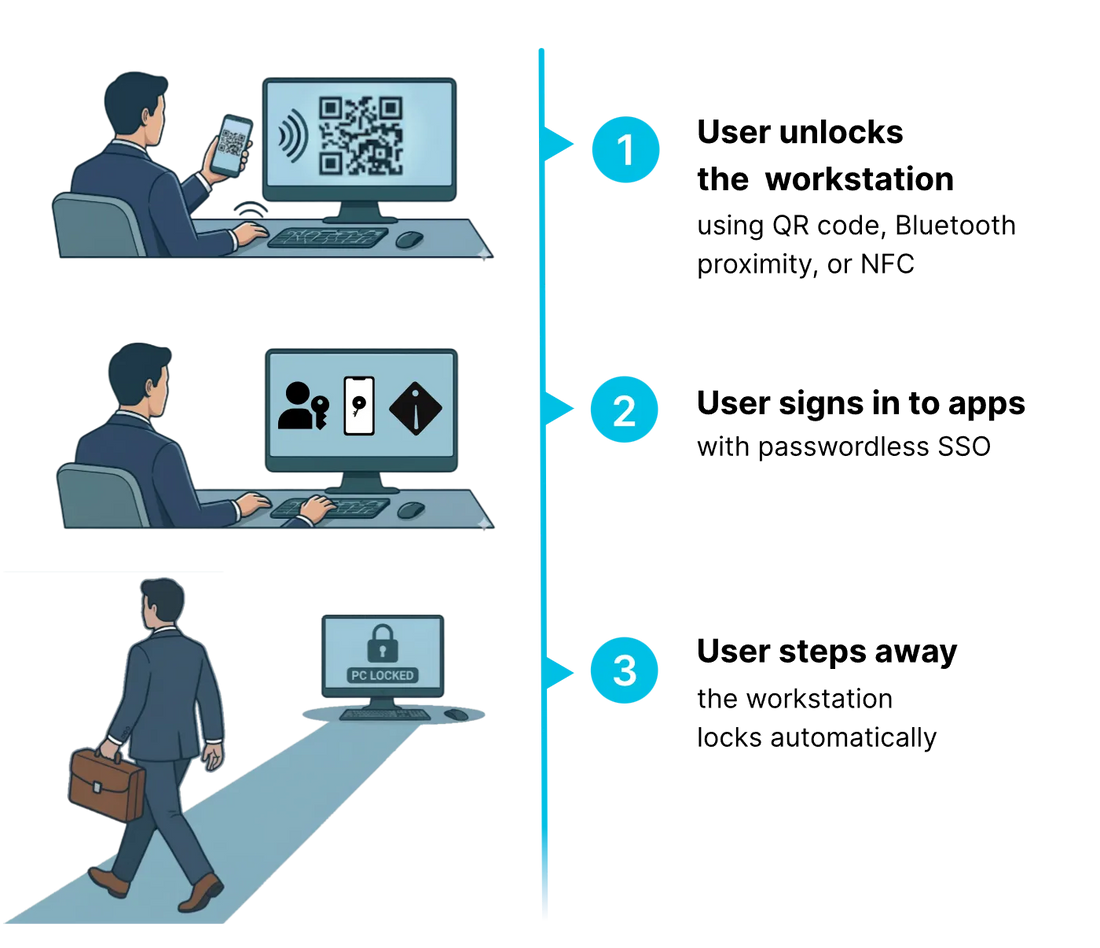
Hideez supports financial services IAM across branches, offices, and operations centers. Employees can unlock shared Windows workstations using QR codes, NFC, or proximity-based methods, then access integrated applications through single sign-on.
- Automatic presence detection
- Contactless workstation access and automatic locking
- Login and logout records for security reviews
Why Hideez?
Hideez IAM solutions for financial services simplify employee access to financial systems while keeping security controls strong. They reduce password-related risks, improve access visibility, and support regulatory compliance without disrupting daily banking operations.
- Active Directory and Entra ID integration. Synchronize users with existing directories and enable centralized account management, including optional password rotation.
- Free trial and proof of concept. Test Hideez in your own IT environment to evaluate authentication workflows before wider deployment.
- Regulatory compliance support. Address PCI DSS and DORA-related security requirements with phishing-resistant MFA, individual user authentication, and auditable login records.
Key Capabilities of Financial Services Identity and Access Management

Shared workstations & branch access
Give tellers and branch staff personal sign-in on shared Windows PCs. Automatic proximity locking helps protect unattended sessions between customer visits.

Passwordless SSO for modern & legacy apps
Connect SAML and OIDC applications to passwordless SSO. Use Hideez AuthShield to extend the same sign-in experience to compatible legacy web apps.

Flexible deployment & compliance support
Deploy on premises, in a private cloud, or in the Hideez cloud. Choose an architecture that fits your data protection, hosting, and oversight requirements.

Privileged access & phishing-resistant MFA
Protect administrator sign-ins to integrated services with FIDO2 MFA. Apply access policies and retain authentication records for security reviews.
Explore our passwordless authentication tools
Choose hardware keys, Hideez Authenticator, or passkeys to match each employee's working environment. Hideez supports IAM for the finance industry with options for branch staff, office teams, and users who need a dedicated hardware credential.

Use employees' smartphones for passwordless authentication across banking applications, web services, and shared workstations. Support secure access in branches, offices, and remote environments without requiring separate hardware tokens for every employee.
Enable employees to unlock Windows workstations without passwords using mobile-based methods such as QR, NFC, or proximity-based login, reducing login friction for staff who move between systems all day while lowering exposure to password theft and reuse.
Automatically lock workstations when employees move away, helping protect sensitive financial data from unauthorized access in branches, operations centers, and offices where unattended sessions create unnecessary risk.

Use FIDO2 hardware keys to enforce strong, phishing-resistant authentication for employees accessing critical banking systems and internal applications.
Enable secure, passwordless login to Windows workstations using hardware keys, reducing reliance on passwords and minimizing credential theft risks.
Deploy FIDO-based multi-factor authentication to protect access to sensitive systems and support compliance with modern security standards.
Securely store and use credentials for legacy banking systems and internal tools that still require passwords or OTP, reducing exposure and simplifying access.
Automatically lock workstations when users step away using Bluetooth-enabled hardware keys, preventing unauthorized access to financial data.
The Hideez Key can also replace smart cards for RFID and NFC-based building access, helping financial organizations simplify and streamline physical access control.

Employees can use a passkey to access supported financial and business web services, confirming sign-in with a fingerprint, Face ID, or a device PIN. Biometric data stays on the device.
FIDO2/WebAuthn binds authentication to the legitimate service rather than a reusable password. With user verification required, a passkey combines possession of the authenticator with a local PIN or biometric check, without asking staff to enter a one-time code.
Hideez supports compatible FIDO2 security keys from other vendors, including Yubico. Staff can use an approved hardware key for supported passkey sign-ins, allowing your organization to retain suitable authenticators already in use.
Hideez vs Duo vs Yubico
| Hideez | Duo | Yubico | |
|---|---|---|---|
| On-prem / self-hosted deployment | Yes | No | No |
| Acts as IdP for passwordless SSO | Yes | No | No |
| Active Directory / Entra ID integration | Yes | Partial | No |
| Authentication methods | Passkeys, Hideez mobile app (QR, Bluetooth, NFC), Hideez Keys (USB, Bluetooth, NFC, RFID) | Passkeys, Duo Mobile, security keys | Passkeys, YubiKey, smart card/PIV, OTP |
| Passwordless web / app login | Yes | Yes | Yes |
| Passwordless Windows login | Yes | Yes | Yes |
| Automatic proximity-based logoff | Yes | Yes | No |
| Works without a mobile phone | Yes | Partial | Yes |
Hardware Security Keys for Financial Institutions
See how finance organizations use Hideez Workforce Identity to protect critical resources from unauthorized access.

Our clients


Our certifications




Questions from financial institutions
How can banks meet MFA requirements without passwords?
Hideez offers several authentication options for banks, including the Hideez Authenticator mobile app with QR, NFC, and Bluetooth-based login, FIDO2 hardware keys such as Hideez Key, and passkeys. FIDO2 keys and passkeys provide phishing-resistant MFA on compatible systems, helping financial institutions support PCI DSS and DORA-related access security requirements.
Do we have to replace our identity provider to use Hideez?
No. Hideez connects to Active Directory or Microsoft Entra ID and syncs users automatically. It also supports FIDO2 security keys from other vendors, including Yubico, so you can combine authentication methods without replacing your existing security stack.
How do branch and operations staff sign in to shared workstations?
Employees unlock Windows workstations with a QR code, an NFC tap, or Bluetooth proximity, with no password typed. The PC locks automatically when the employee walks away. It works with closely placed devices, offline scenarios, and RDP. Device login is Windows-only.
Can Hideez handle legacy banking systems that still require passwords?
Yes. Hideez Key can securely store and fill credentials for legacy banking systems and internal tools that still need passwords or one-time passwords. Passwordless SSO also covers web services that do not natively support SAML or OIDC.
Where can Hideez be deployed, and can we test it first?
Deploy Hideez on premises, in a dedicated private cloud, or in a multitenant cloud hosted in the US or Europe. You can start with a free proof of concept to validate key access scenarios in your own environment before wider rollout.
How does Hideez help financial institutions comply with PCI DSS 4.0.1 and DORA?
Hideez supports access-related controls through strong authentication, access policies, automatic workstation locking, and audit logs. PCI DSS and DORA compliance also depends on your risk management, configuration, and documented procedures.
What happens if an employee loses their Hideez security key?
Revoke the lost key's access in Hideez and remove its registration from services where it was enrolled directly. Restore access after identity verification using an approved backup method or a replacement key.
Enhance financial services IAM with Hideez
Discuss identity and access management for financial services with a Hideez specialist. Share your application list and access requirements to help us identify a suitable deployment approach.